
Keeper links Tenable scans to instant cloud remediation
Wed, 28th Oct 2026 (Today)
Keeper Security has launched native integrations with Tenable, designed to connect cloud risk detection and remediation in a single workflow.
The integrations let security teams send findings from Tenable into Keeper, then take actions such as rotating credentials, enforcing Just-In-Time access and removing standing privileges. The process can be completed without switching platforms or handling manual tickets.
Tenable's tools identify exposed identities, risky access paths and cloud misconfigurations. Keeper is positioning the integration around the gap that often exists between identifying those issues and getting changes approved and applied across production systems.
Once a finding reaches Keeper, the platform can trigger a remediation step and notify Tenable when the action is complete. This closes the loop between detection and resolution while updating the finding status automatically.
Another part of the integration focuses on how credentials are handled during vulnerability scans. Organisations often store passwords or SSH keys in scan policies so scanners can log into systems and carry out deeper checks. The new setup allows those credentials to be stored centrally in Keeper, with Tenable requesting them at scan time rather than holding them in policy configurations.
This applies to scans across SSH, Windows and database environments. Credentialed scans are widely used because they give security teams visibility into installed software versions, configuration settings, patch levels and compliance status that may not be visible in unauthenticated scans.
Closing the gap
The integrations are aimed at cloud security operations teams managing large estates and facing delays between discovery and action. In many organisations, remediation still involves separate tools, approval chains and ticketing systems, leaving vulnerabilities unaddressed for days or weeks.
Keeper said its architecture keeps the exchange of findings and credentials inside the customer environment. It uses a self-hosted gateway called Keeper Encrypter to receive webhook traffic from Tenable and encrypt the data exchange with customer-managed private keys.
According to Keeper, that means cloud infrastructure does not handle unencrypted findings or credentials during the process. Every remediation action is also logged to provide an audit trail and compliance visibility.
For infrastructure-related findings, users can rotate credentials across databases, machines, cloud environments and directories. For access-control issues, teams can apply Just-In-Time access to reduce standing privileges. Keeper also said cloud identities flagged by Tenable can be onboarded as PAM user records without separate database, machine or directory resources.
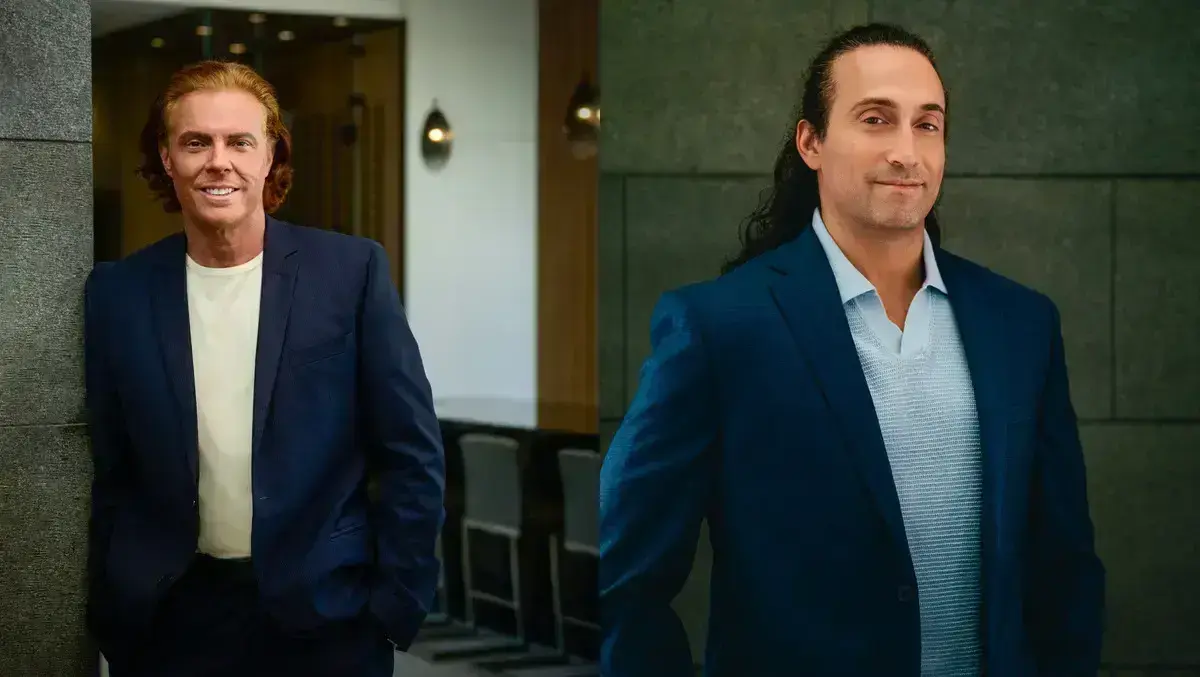
"Organisations can't remediate findings if they aren't properly equipped to take action immediately," said Darren Guccione, Chief Executive Officer and Co-founder of Keeper Security.
"As AI-powered threats increase the onslaught of cyber attacks and decrease the window of time in which cyber defenders can take action, this integration enables cloud security teams to implement fixes in seconds instead of weeks," Guccione said.
Credential handling
The second integration connects Tenable with Keeper Commander, the vendor's management interface. Its purpose is to separate scanning tools from long-lived credentials while still allowing authenticated scans to run.
Credentials can rotate automatically in Keeper, with Tenable retrieving updated values the next time a scan runs. That removes the need for administrators to update scan policies manually after password changes.
This matters because credentialed scanning remains a standard method for assessing internal systems in greater detail. Security teams typically rely on those checks to verify software versions, patch status and system configuration across servers and databases.
"By connecting Tenable's cloud detection directly to Keeper's zero-trust remediation engine, we've built a closed-loop workflow that operates entirely within the customer's perimeter," said Craig Lurey, Chief Technology Officer and Co-founder of Keeper Security.
"Security teams can immediately execute targeted fixes - from automated credential rotation to JIT access enforcement - without leaving their workflow or exposing unencrypted data," Lurey said.
The integrations are available to Keeper customers with active KeeperPAM licences.