Incident Response stories
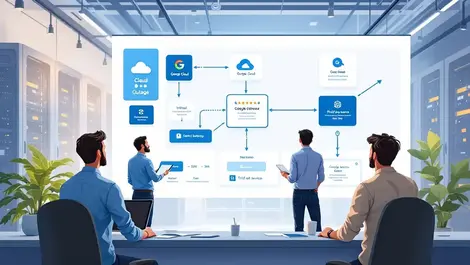
Customers can use the six-step workflow to tell whether an outage stems from Google, their own systems or a third-party service.
Attackers are exploiting AI tools to speed intrusions and drain cloud resources, pushing defenders towards machine-speed security operations.
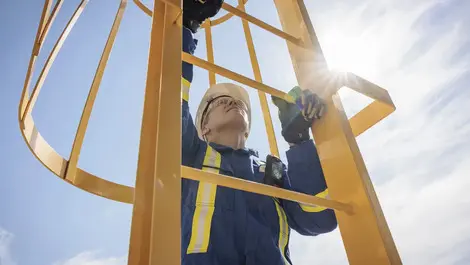
Early customer adoption of the G8 wearable is bolstering Blackline Safety's push to sell one device for monitoring workers in hazardous sites.
Criminals are increasingly using AI for ransomware and credential theft, while flaws in test models are exposing production systems and data.
Autonomous systems are now creating fresh avenues for code theft, remote execution and runaway cloud spending, Mandiant says.
Enterprises face mounting risks from AI outages and hidden governance costs as Forrester says day-to-day operational needs now outrank frontier fears.
Security teams can now compare validated exposure findings with endpoint and cloud telemetry after Horizon3 tied NodeZero into CrowdStrike's SIEM.
European businesses are facing rising costs and audit risk as overlapping AI, data and cyber rules force separate assessments for the same incident.
Existing customers can access AI-driven troubleshooting without a higher base price, as Riverbed bundles new observability tools into Network 360.
Ageing technology is leaving critical services exposed as AI lets attackers exploit known weaknesses at machine speed, experts say.
Australian firms face rising cyber risk, with 80% hit in the past year and only 2% confident their recovery plans can withstand frontier AI threats.
With most operators exposed to basic flaws, the paper warns telecom networks could face the same low-effort intrusions seen in US water systems.
Engineering teams face a governance gap as AI agents begin handling production changes, prompting tighter controls over access, audits and permissions.
Criminal access to thousands of Microsoft accounts was cut off after the companies shared threat data through the Global Signal Exchange.
Mid-market clients should gain broader threat visibility and tighter remote access control as Thrive upgrades its managed security platform.
Canadian firms are being hit by ransomware at 18.2% versus a 9.0% global average, with web-delivered attacks now overtaking email.
Most US companies lack full trust in AI, with governance and accountability systems struggling to keep pace with adoption.
US banks are under pressure to prove systems can be restored quickly as regulators and counterparties demand tested resilience, not paper plans.
Orient will spend USD $5 million as the deal aims to deepen Securonix's India reach and add 100 cybersecurity hires in Mumbai.
Businesses have almost no time to patch flaws now, as ESET says the median gap between disclosure and exploitation fell to zero days in 2026.