Container Security stories
Private cloud operators may cut hardware costs by a third as Broadcom folds AI-assisted threat prevention and API security into VMware tools.
Teams running AI agents at scale could save idle compute and tighten isolation as Google opens Agent Substrate on Kubernetes Engine.
Australian firms could face faster breaches as model-driven attackers shrink exploit times to hours, making containment and zero trust vital.
Defenders now have minutes, not hours, as attackers use agentic AI to automate credential theft, scanning and extortion across live operations.
Customers will get human-verified open source fixes as Broadcom expands Spring security coverage and counters risks from AI-generated patches.
The experimental setup lets AI teams run untrusted model code in isolated Ray clusters on Google Kubernetes Engine without exposing host containers.
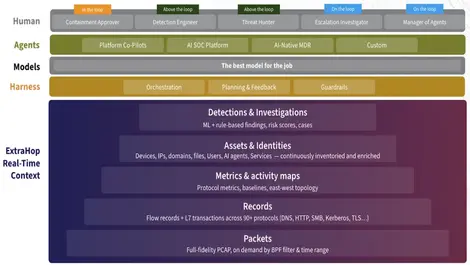
Security teams face wider blind spots as ExtraHop's new sensor brings full inspection of 400 Gbps data centre traffic to RevealX.
Growing use by major tech groups is helping open source secrets manager OpenBao win trust as cloud and AI credential risks mount.
Researchers can claim up to USD $1 million for breaking Vercel Sandbox's isolation, as the cloud provider opens its boundary to public scrutiny.
The accreditation strengthens Adfinis's hand with customers seeking secure open source tools for hybrid cloud systems and digital sovereignty.
The preview could help GKE users enforce cluster-wide security without clashing with namespace rules, especially in multi-tenant environments.
Security teams could spot newly disclosed flaws within minutes as rising CVE volumes and faster attacks squeeze response windows.
Tests on an n2-standard-48 virtual machine showed Google Cloud's sandbox and orchestration tweaks could cut per-agent costs by up to 75%.
The tool aims to help developers cut vulnerability backlogs and reach no exploitable flaws within 90 days as AI coding expands risk.
Joint users of Kubernetes can now move from finding vulnerabilities to hardening container images faster as the gap to exploitation narrows.
Rising use of AI coding tools is widening software supply-chain risks for businesses across the Middle East, Türkiye and Africa.
Security teams can now track newly disclosed CVEs in live systems, as RapidFort expands its supply chain tools into production monitoring.
The update aims to cut remediation costs and stop teams wasting time by re-analysing vulnerabilities without enough business context.
Open source package attacks can now be blocked earlier, as NetRise brings trust checks into editors, command lines and AI coding tools.
Security teams can now automate triage and remediation as risks emerge, with early access to AI agents that still require human oversight.