

Blackpoint adds identity threat tools to CompassOne
Wed, 23rd Sep 2026 (Today)
Blackpoint Cyber has added identity threat detection and response features to its CompassOne platform, expanding its tools for Microsoft 365, Google Workspace and Cisco Duo environments.
The update includes a historical scan for Microsoft 365, nine new detections, automated response controls and new incident reporting tools. The additions are intended to identify identity-based attacks earlier, contain threats with less disruption and improve post-incident records.
Identity-based attacks are a growing concern for security teams as attackers increasingly rely on stolen credentials, compromised mailboxes and social engineering rather than malware alone. Email compromise and misuse of legitimate sign-in systems can make these intrusions harder to spot because they often resemble normal user activity.
Among the new detections are six for Microsoft environments: Suspicious Sending Pattern, Anomalous Token, Attacker in the Middle, Possible PRT Access, Verified Threat Actor IP and Suspicious Browser Sign-In. Blackpoint has also added two detections for Microsoft Teams that look for helpdesk impersonation chats and tenant-name spoofing attempts.
Another detection targets device code phishing, flagging sign-ins that use Microsoft's device code authentication flow when the pattern is consistent with phishing, even if the login otherwise appears legitimate.
Response tools
Blackpoint has also expanded its automated response options. Geo and VPN Policy Automation can block logins from unapproved countries or commercial VPNs as they occur, while allowing policy updates to be applied in bulk across managed tenants.
For Google Workspace customers, a new Auto Logout option ends a compromised session and resets the account password while keeping the user's mailbox and calendar active. The aim is to avoid the access loss and disruption that can follow a full account shutdown.
New visibility tools also track account and policy changes. User Disabled Notifications send real-time alerts when CompassOne disables an account across Microsoft 365, Google Workspace or Cisco Duo, including the affected user, the actor behind the action and the reason.
ITDR Policy Change Visibility shows who last changed a geo or VPN policy and when. The information appears directly on the Cloud Response policies page, giving administrators an audit trail for configuration changes.
Historical scan
A notable part of the update is the Historical Scan Report for Microsoft 365 onboarding. The tool provides a retrospective view of up to 180 days of activity to help organisations assess whether an attacker may already have access to the environment.
The report includes AI-driven analysis, MITRE ATT&CK mappings and remediation guidance ranked by priority. Blackpoint has also introduced a Forensic Report that generates a customer-ready PDF once a Microsoft 365 incident has been contained, including an attacker timeline, a blast-radius summary and exfiltration tracking.
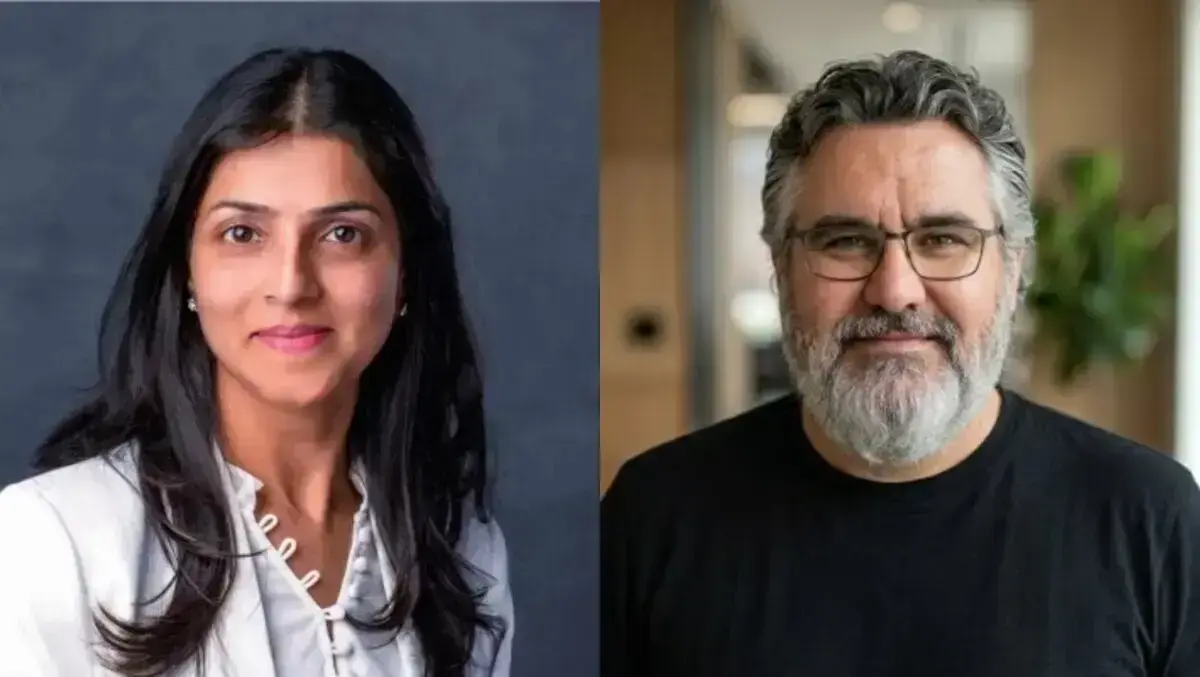
William Kapes, Director of Technical Operations at Integritek, described the operational burden some security tools can place on internal teams.
"A compromised mailbox is not an inconvenience; it's a confidentiality problem with our clients' own clients attached to it. Much of what we saw when evaluating the competition was alerts dressed up as detection, which just moves the work back to us. Blackpoint's SOC investigates and acts, and every addition has been aimed at taking work off my team rather than handing them another dashboard to check," said Kapes.
Blackpoint linked the expansion to a broader shift in the threat landscape, where identities have become a common entry point into corporate systems. Security providers have increasingly focused on account behaviour, sign-in anomalies and cloud service misuse as attacks move away from traditional endpoint compromise.
Sasmita Panda, Vice President of Engineering at Blackpoint Cyber, said the company sees identity as a central area of risk.
"Threats are becoming agentic, and identities are the new threat vector where attackers are entering the business," said Panda. "We aren't here to merely defend, we are here to protect, and that requires more than adding another detection rule-it requires the ability to continuously recognize new attack patterns, make sense of identity activity in context, and act immediately. Our expanded ITDR capabilities and newly launched ITDR AI SOC Agent are a powerful combination of machine-speed detection and containment with the expertise of our human AI-accelerated SOC. That allows us to respond to identity threats in an average of under 2 minutes and as fast as 21 seconds without losing the judgment, accountability and precision that effective incident response demands."
Blackpoint focuses on small and mid-sized businesses and managed service provider partners, a segment that often has fewer in-house security resources than larger enterprises. In that context, automation, managed investigation and clearer reporting can carry particular weight for service providers overseeing multiple customer environments at once.
The latest additions also reflect a broader push across the cybersecurity sector to produce more structured evidence after incidents, as customers and insurers seek clearer records of what happened, what data may have been exposed and what steps were taken in response.
The Historical Scan Report covers up to 180 days of Microsoft 365 activity during tenant onboarding.